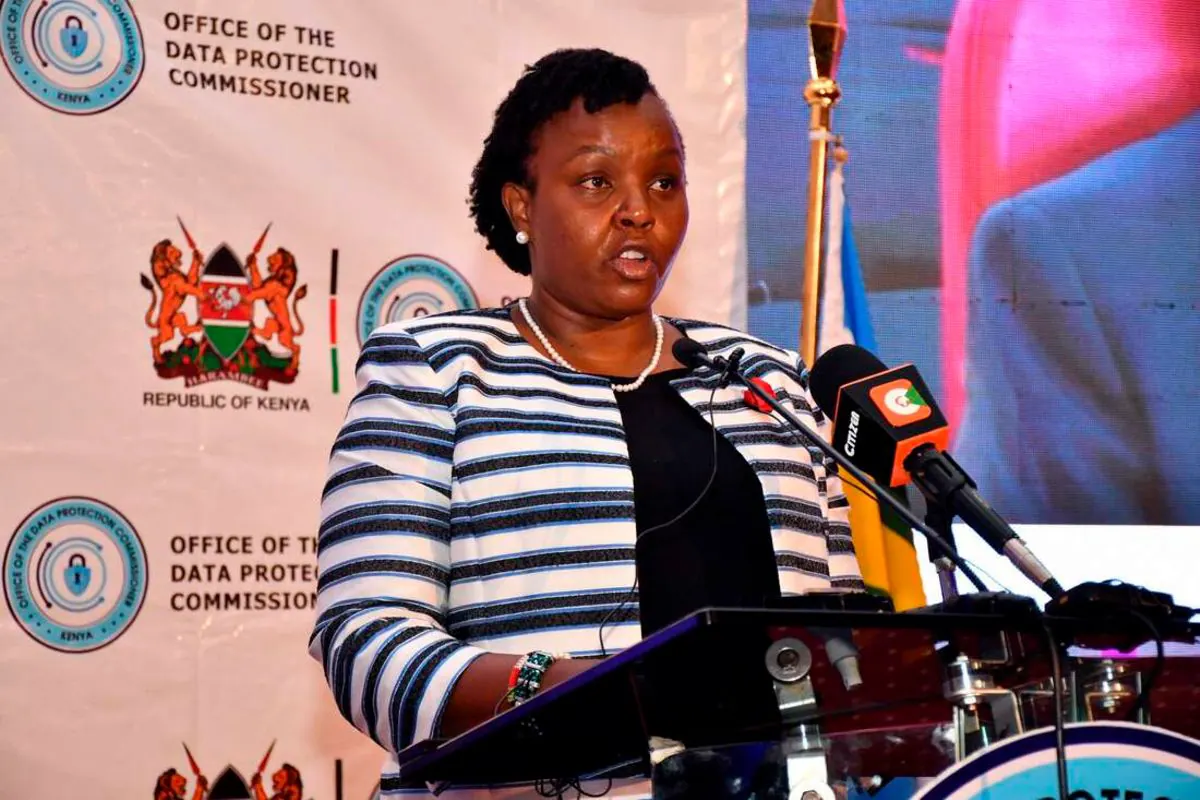
Outgoing Data Commissioner Immaculate Kassait announced that a deal with Moldovan firm B2bhint has resulted in the permanent deletion of stolen data belonging to more than two million Kenyan businesses, ending an 18-month probe into the largest data breach involving a government entity in Kenya’s history.
B2bhint accessed the Business Registration Service’s IT system in February last year by exploiting a bug, obtained sensitive details of significant shareholders and sold over eight million items at prices ranging from KSh24 million per package to as little as $0.015 (two shillings) for telephone numbers, valuing the stolen data at KSh2.4 billion.
Kassait said the Office of the Data Protection Commissioner enlisted the goodwill of the European Union Commission and the Moldovan data protection authority to locate the data controller and compel it to delete the information, adding “In the case of BRS, when we wrote to the person behind the breach, they pushed back, and one of the issues is that we didn’t have mutual legal assistance to pursue them.”
A spokesperson for B2bhint confirmed that, after being contacted by Kenyan and Moldovan authorities, the company responded and permanently deleted the data.
The leaked data set included 812,863 phone numbers, 832,648 email addresses, 2,091,046 physical addresses and the status of 2,093,194 firms, and those who purchased the information before deletion may still retain it, although it has not resurfaced publicly.
The breach revealed the holdings of President William Ruto’s family, the Kenyatta family and the Odinga family, listing businesses such as Weston Hotel and Koilel Farm for the Ruto family, Heritage Hotels, Brookside and Emken Investments for Muhoho Kenyatta, and East Africa Spectre, Spectre International, Lennox Development and other firms for the Odinga family.
Kassait said the regulator investigated the breach, issued an enforcement notice to the Business Registration Service identifying system gaps and requiring improvements, and noted that the agency had implemented the recommendations, so no penalty notice was issued.
Under the Data Protection Act, 2019, data controllers must notify the commissioner of a breach within 72 hours and inform affected individuals, and the commissioner is empowered to issue enforcement notices and administrative fines.
Kassait will retire after completing her six-year term and will be succeeded by Lydia Sitienei, the former head of legal at the Communications Authority of Kenya.