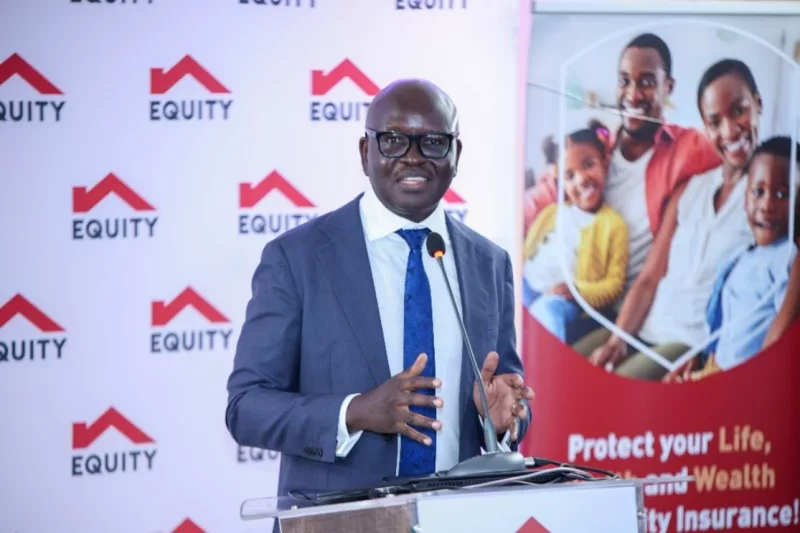
At a Cyber Risk Awareness Forum in Nairobi, Kenyan businesses were urged to adopt cyber risk insurance as AI-driven attacks surge.
Fidelis Muia, Director of Technical Services at Kenya Bankers Association, said reliance on digital technologies has raised exposure for large corporates and SMEs, and called on banks and their corporate partners to stay proactive.
He listed the main threats as social engineering, phishing, impersonation, mobile-money fraud, SIM swaps, malware and vulnerabilities from third-party service providers.
The Communications Authority of Kenya recorded 3.37 billion cyber-threat events in the first quarter of 2026, equivalent to about 433 attacks each second.
Interpol’s 2026 Global Financial Fraud Threat Assessment found AI-enabled scams are 4.5 times more profitable than traditional methods, a trend fuelled by the growth of Fraud-as-a-Service, which supplies tools for deep-fake audio, voice cloning and automated phishing.
A September 2026 Forensics Digest by PwC highlighted four challenges for organisations – speed, skills, visibility and trust gaps – and noted that deepfakes and synthetic identities are undermining document, facial and voice verification.
The digest added that “AI is no longer just a tool for efficiency; it is reshaping both sides of the cybersecurity battlefield.”
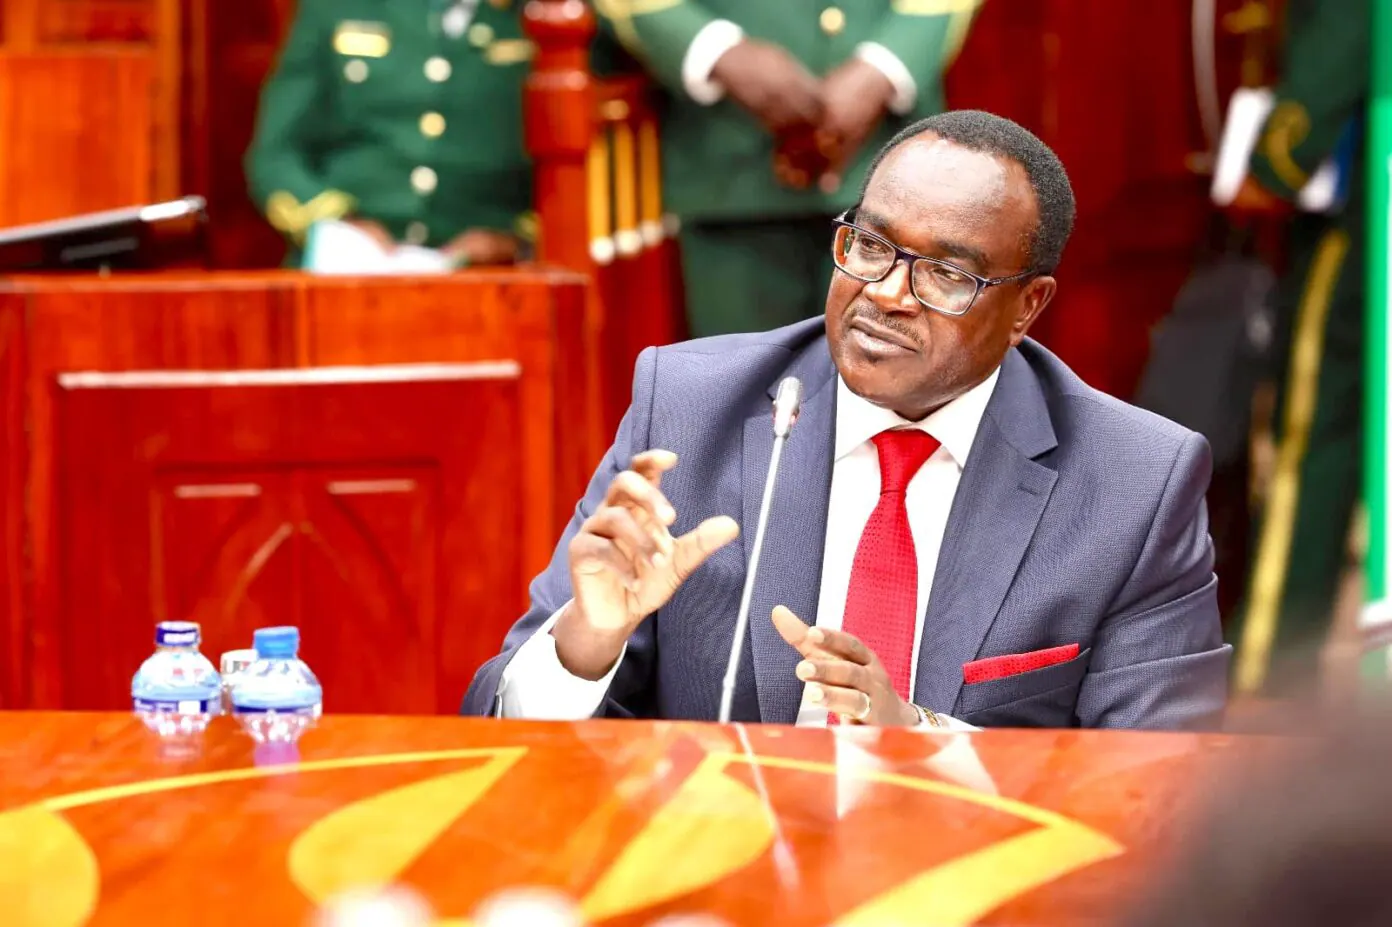
Equity Bank Kenya Managing Director Moses Nyabanda warned that ransomware and sophisticated AI-enabled cybercrime expose individuals, businesses and government institutions, stating “No business is immune, especially at a time we all transact digitally. With its sophistication, AI has changed the fundamentals of cyber risk management and has significantly increased the scale and likelihood of attacks.”
Nyabanda urged firms to focus on core controls and to stress-test them against AI-enabled scenarios.
Industry leaders at the forum said cybersecurity must move from an IT function to a boardroom priority, with senior management and boards overseeing cyber risk.
They argued that while preventive technology and employee training remain essential, they cannot eliminate risk entirely, and recommended specialised cyber risk insurance as a mandatory last line of defence.
Such policies cover data breaches, network security failures and business interruptions, as well as system-recovery costs, regulatory liabilities, operational disruptions and losses from compromised customer data.
Leaders concluded that resilience in an AI-driven digital economy requires a combination of intelligent threat detection, disciplined human verification and the financial safety net of cyber insurance, and called for regular review and strengthening of risk-management frameworks.